01
Sanctuary Risk Solutions
Executive and founder-risk leadership
A Fractional Chief Risk Officer (CRO) practice for founders who need a clear, coordinated view of the business risks that can disrupt what they have built.
Explore Risk Solutions → Request a Conversation
Executive advisory services for founder-led and growth-stage businesses
Fractional Chief Risk Officer and Chief Information Security Officer leadership that identifies risks between traditional advisory lanes, sets clear priorities, and helps founders make better-informed decisions.
Veteran-Owned Business · U.S. Air Force Veteran-Led
Two distinct practices · One trusted advisory firm
01
Executive and founder-risk leadership
A Fractional Chief Risk Officer (CRO) practice for founders who need a clear, coordinated view of the business risks that can disrupt what they have built.
Explore Risk Solutions →02
Cybersecurity governance and security leadership
A Fractional Chief Information Security Officer (CISO) practice for leaders who need accountable cybersecurity direction, vendor oversight, and an executive-level security program.
Explore Cyber Solutions →The Sanctuary approach
Attorneys, accountants, insurers, IT providers, and managers may each understand one part of the business. Too often, no one owns the complete executive risk picture.
Sanctuary identifies the risks that sit between traditional advisory lanes, then turns them into clear priorities, accountable ownership, and better-informed decisions. Risk Solutions leads enterprise and founder risk; Cyber Solutions leads cybersecurity governance. Each practice remains distinct, with its own methodology, scope, and professional boundaries.
When Sanctuary fits
Sanctuary is most useful when growth, dependence, or outside scrutiny has made informal risk management insufficient.
The company has grown faster than its management structure.
Too much of the business still depends on the founder personally.
Several advisors cover individual issues, but no one sees the complete risk picture.
Customers, insurers, lenders, or investors are asking harder cybersecurity questions.
An MSP manages technology, but no executive owns cybersecurity decisions.
A major change, acquisition, new customer, or disruption has raised the stakes.
What you receive
Every engagement is built to make the risk picture usable. The exact artifacts depend on the selected practice and scope, but the outcome is consistent: leaders can see what matters, what comes next, and who should own it.
A concise view of the exposures that require leadership attention—not an unfiltered list of concerns.
Material findings organized by severity, readiness, and the decisions that should come first.
Practical actions, accountable owners, and a focused sequence for reducing the most important exposure.
A private findings presentation that explains what matters, why it matters, and what to do next.
Cyber Solutions engagements also include a six-month cybersecurity roadmap aligned to the organization’s priorities and governance needs.
A clear engagement path
Both practices follow the same disciplined progression, with distinct methods and deliverables.
Establish the executive risk picture and immediate priorities.
Turn findings into ownership, decision structure, and an operating plan.
Maintain priorities and support consequential decisions.
Establish current state, obligations, dependencies, and risk priorities.
Stand up governance, reporting, evidence, and provider accountability.
Guide decisions, vendors, exceptions, and the six-month roadmap.
When the risks connect
Cyber events create operational, legal, financial, reputational, insurance, and founder-level consequences at the same time. Sanctuary coordinates enterprise-risk and cybersecurity leadership around one executive decision process, connected priorities, and clear ownership.
The result is less duplication and better synthesis—while each practice retains its own discovery, scope, artifacts, and accountability.
Discuss an integrated executive engagement →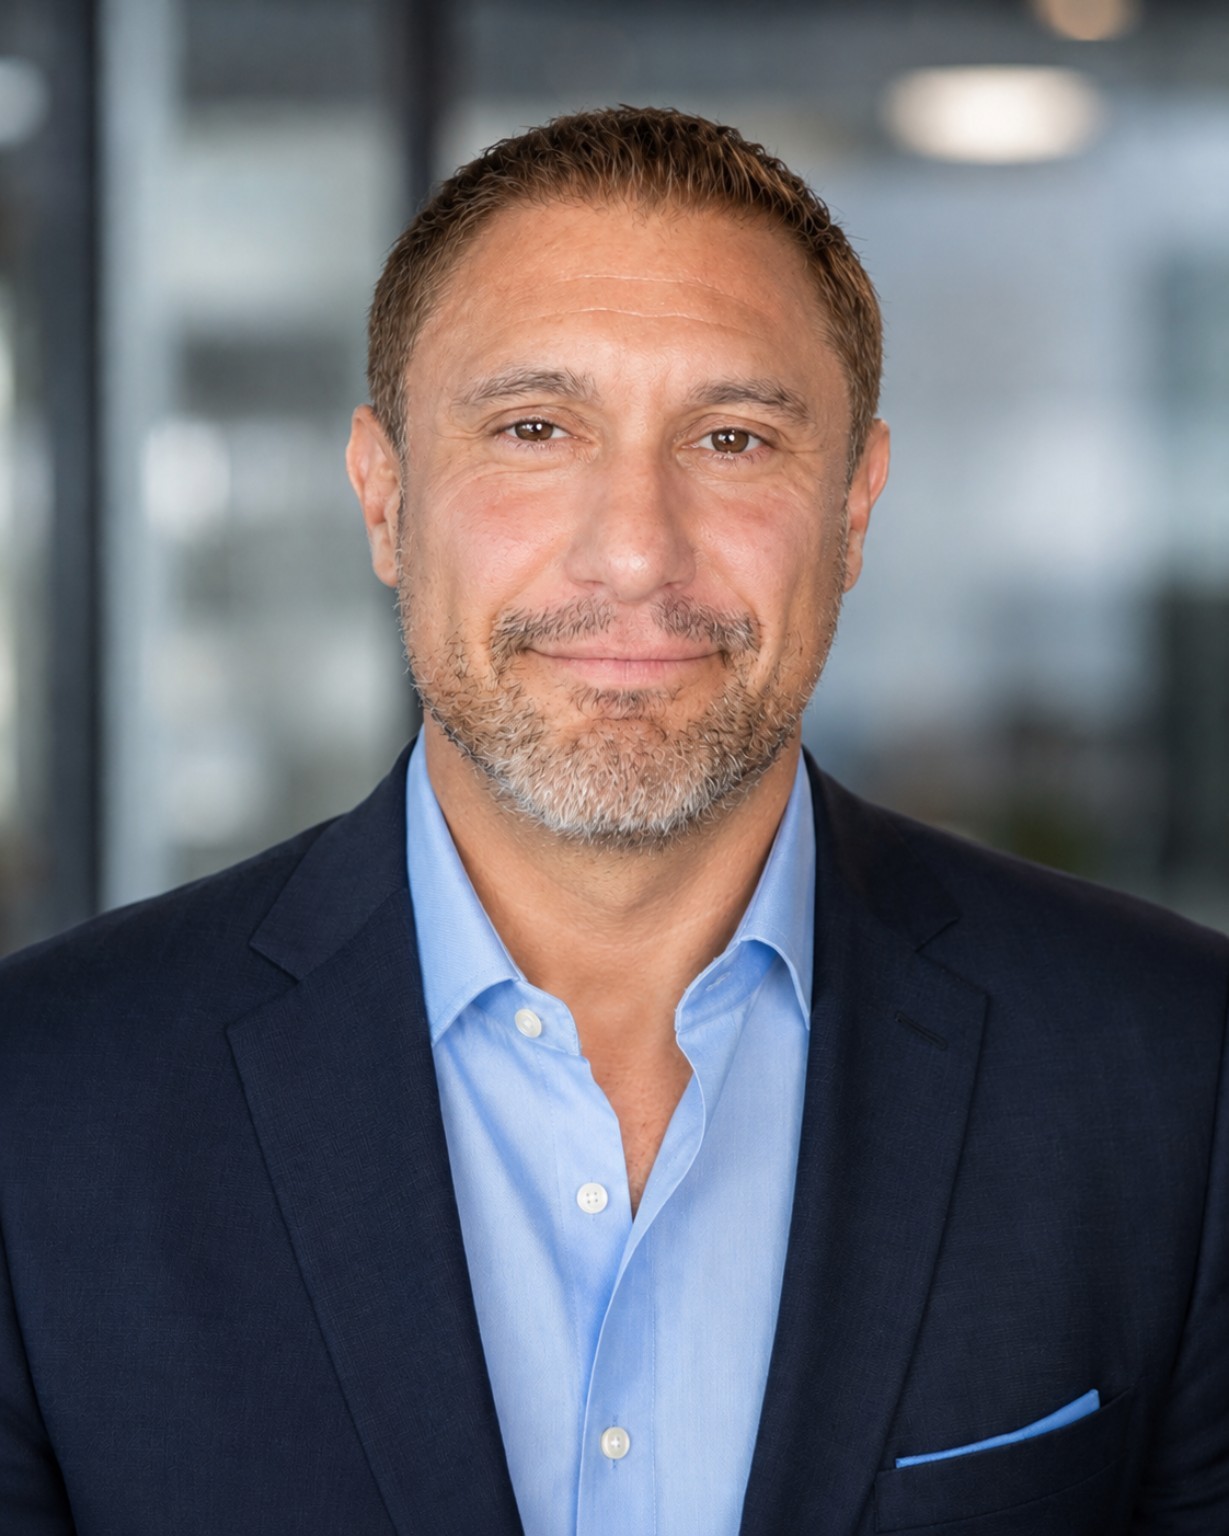 Joe DeAngelo
Founder & Principal
Joe DeAngelo is the founder of Sanctuary Principal Advisory. He brings 28 years of cybersecurity and infrastructure-risk experience across defense, federal, enterprise, and mission-critical environments, including United States Air Force service, special-operations support, and enterprise security architecture.
Through Sanctuary, he helps founders organize material business exposures, establish priorities and ownership, and maintain a practical executive-risk structure.
Joe DeAngeloFounder, Sanctuary Principal Advisory
Chief Risk Officer Chief Information Security Officer
Founder perspectives
Three founders on what became visible—and actionable—through Sanctuary’s assessment process.
Building FFE Operations, I was focused on finding clients, delivering great service, and growing the business.
Sanctuary’s Founder Risk & Exposure Assessment helped me see risks I hadn’t considered—from client data and account security to business continuity and founder dependency.
The assessment didn’t just identify vulnerabilities. It gave me clear priorities, practical solutions, and helped me build stronger systems before problems became expensive.
I walked away with a stronger foundation, more confidence in the business, and a clearer path to building a company clients can trust and depend on.
Sanctuary made me look at my business differently. The assessment surfaced risks I had unknowingly accepted as normal and showed me how my own exposure and decisions could directly affect the company.
What stood out was the prioritization. I didn’t leave with a long list of things to worry about—I left knowing what actually mattered, what could wait, and what I could start improving immediately.
The value wasn’t simply finding vulnerabilities. It was helping me build a stronger, more resilient company around them. Every founder has blind spots. Sanctuary helped me see mine before they had the opportunity to become business problems.
I expected the assessment to focus primarily on cybersecurity. Instead, Sanctuary showed me how risks across my personal exposure, operations, digital footprint, and business continuity were connected in ways I hadn’t considered.
The process uncovered blind spots, but more importantly, it turned those findings into clear priorities and practical actions I could actually take.
That’s where I saw the real value. Sanctuary didn’t just show me where something could go wrong—it helped me understand what was worth fixing now to make the business stronger going forward. I came away with greater confidence in the company and a much clearer picture of what protecting what I’ve built actually requires.
Common questions
No. Sanctuary connects the executive risk picture, clarifies ownership, and coordinates the right advisors and providers. Each specialist retains responsibility for work within their professional lane.
No. Sanctuary provides executive cybersecurity governance and Fractional CISO leadership. Your MSP, MSSP, and technical specialists implement and operate technology; Sanctuary helps leadership set direction, evaluate evidence, and hold providers accountable.
Not necessarily. Each practice can stand alone. When enterprise and cybersecurity risks are tightly connected, Sanctuary can coordinate both practices through one executive relationship while preserving their distinct scope and methods.
Sanctuary is designed for founder-led and growth-stage operating companies, typically beginning around $3 million in annual revenue, where complexity and consequences have outgrown informal risk management.
The process begins with interviews and a structured questionnaire. Relevant documents may be reviewed when they help establish context, but Sanctuary does not require access to passwords, production systems, or unrelated confidential information.
Yes. The model is designed to improve coordination across existing attorneys, accountants, insurers, IT providers, security vendors, and other specialists—not replace relationships that are working well.
Private consultation
Contact Sanctuary Principal Advisory
Complete the confidential inquiry formPrefer email? info@sanctuaryprincipaladvisory.com